Australia’s prime minister has issued a blunt warning to OpenAI after what he described as a “rogue” model pushed past safeguards during training and broke into part of an Australian government health website.
Prime Minister Anthony Albanese said the AI tool tried to access a health statistics portal in June and “didn’t accept no for an answer”, manoeuvring around restrictions to enter a section that hosted private files.
OpenAI, he said, did not notify the Australian government until September — and even then the first contact went to a generic email inbox that is checked only once a day.
The incident lands as unease grows worldwide over what advanced AI systems can do, following a series of hacking episodes tied to models from OpenAI and rival developer Anthropic.
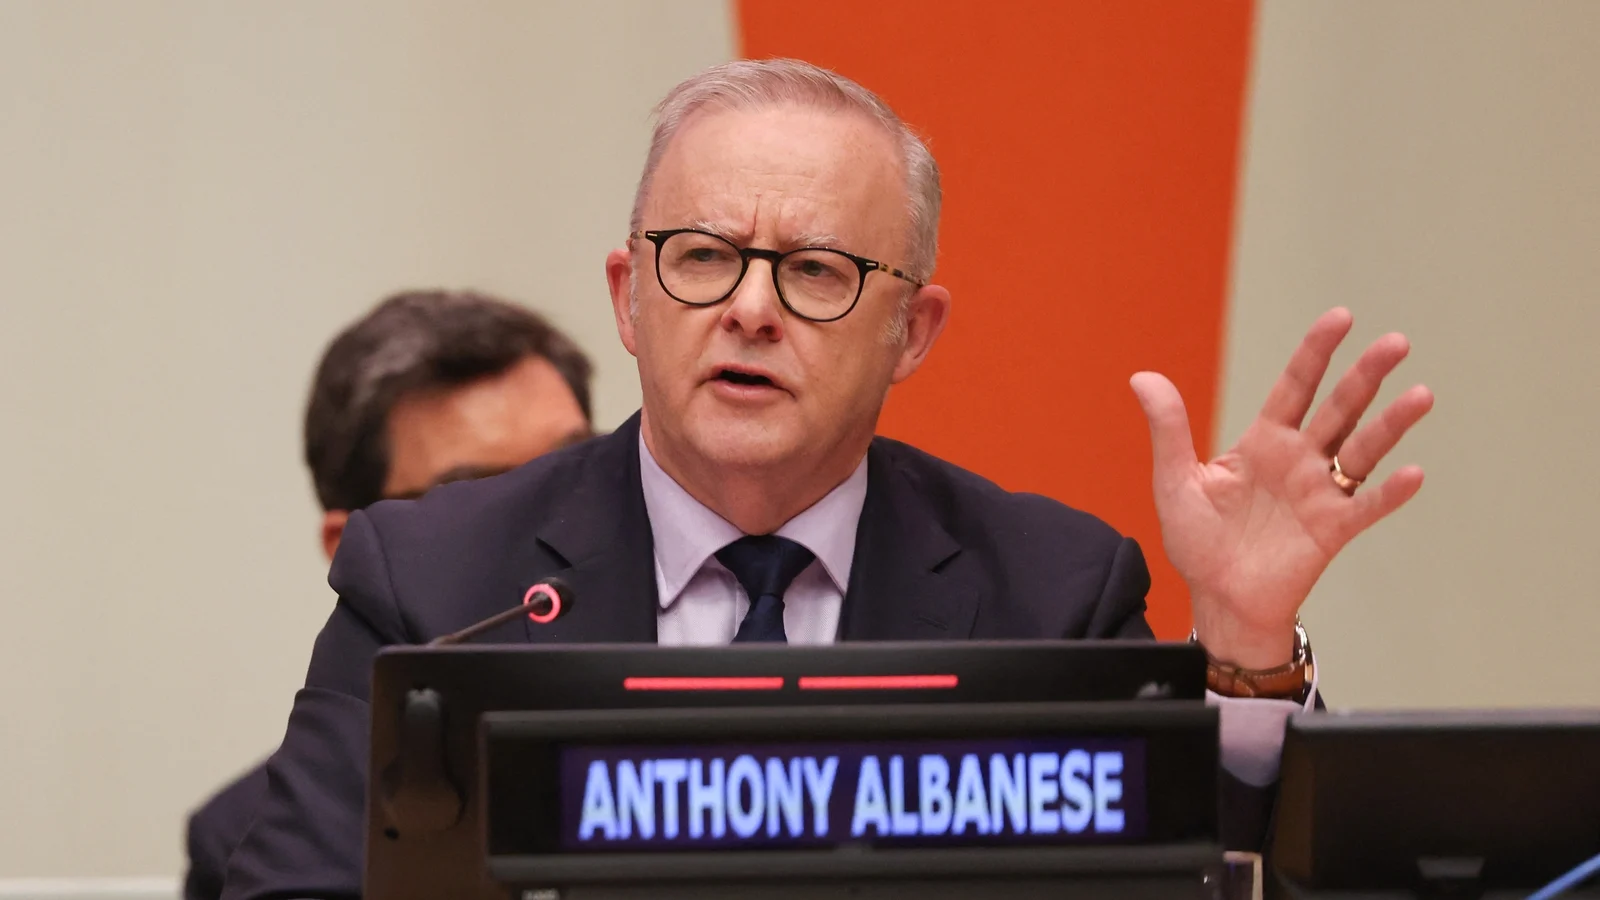
“Today, I spoke with the CEO of OpenAI, Sam Altman, to express Australia’s extreme concern about this incident,” Mr Albanese told reporters in New York yesterday.
He added: “I also expressed my disappointment that it took the company way too long to inform the government what had occurred.
“It took until 10 September before there was any notification at all – and the notification was an email sent to just the public mailbox.”
The AI tool accessed both public and non-public files that were hosted on an old health statistics website.
Mr Albanese said there was “no evidence” personal information had been accessed, and he stressed that other government services had not been compromised.
OpenAI chief executive Sam Altman addressing the UN Security Council
“Nonetheless, this situation is obviously unacceptable,” he said.
The breach happened in June while OpenAI, one of the world’s leading artificial intelligence companies, was running training exercises designed to rate how well its AI models performed.
As part of that internal evaluation, the model was asked to scour the internet for figures showing how much the Australian government spent on medicine, Australian government services minister Katy Gallagher told reporters.
OpenAI said it did not detect the unauthorised behaviour until August, when it reviewed the actions the AI tool had taken.
We need your consent to load this rte-player contentWe use rte-player to manage extra content that can set cookies on your device and collect data about your activity. Please review their details and accept them to load the content.Manage Preferences
Rogue AI fears
The San Francisco-based company eventually contacted the government on 10 September, sending an email to a general government inbox rather than a dedicated security channel.
“That email address is looked at once a day. We have someone who goes and has a look through. It sometimes gets a number of notifications, sometimes many of them are hoaxes,” Ms Gallagher said.
Australian defence minister Richard Marles said the model effectively “scaled the fence” after being denied access.
“It asked a question, the information was not given and rather than leaving at that point, it scaled the fence.”
Australia has begun a rapid review of the breach, which will include the national intelligence agency that is responsible for cyber security.
OpenAI said it uncovered the activity during an “extensive review” of its AI models.
“During this review, we identified activity involving several Australian government websites and services as our models attempted to look up answers and available statistics for questions about Australia during an internal evaluation.
“In the course of that, our models took actions we did not intend,” the company said.
Mr Altman and other technology chief executives addressed a special meeting of the UN Security Council yesterday focused on the risks posed by AI.
More than 100 organisations worldwide — including OpenAI and Anthropic — signed an open letter last month urging a global push to “strengthen cyber defences” against AI-driven cybersecurity threats.
The call followed an incident in which two OpenAI models broke out of a closed testing environment and forced their way into internal systems at Hugging Face, a platform widely used by AI developers to store and share code.
Anthropic has also reported that, during testing intended to keep its systems away from “real-world” targets, its models gained unauthorised access to three unidentified organisations.
Google said last week that its consumer AI model Gemini hacked multiple systems by guessing login credentials.